Scenario :#
A Windows forensics challenge prepared by Champlain College Digital Forensics Association for their yearly CTF.

Windows Image Forensics Case created by AccessData® FTK® Imager 4.2.1.4

Acquired using: ADI4.2.1.4

--------------------------------------------------------------

Information for F:\DFA_Windows\DFA_SP2020_Windows:Setup#
Tools#
Linux : AD1-tools https://github.com/al3ks1s/AD1-tools Windows : TKimager https://www.exterro.com/digital-forensics-software/ftk-imager
Je suis sous linux :
dpkg --install ad1tools_1.0.0-1_amd64.debMonter l'image#
Créer le dossier de travail
mkdir /tmp/ForensicMonter l'image .ad1 avec ad1mount (ReadOnly)
ad1mount -i ~/Downloads/Forensics/CorprateSec.ad1 -m /tmp/ForensicExtraire l'image pour pouvoir intéragir avec
sudo mkdir /tmp/AD1_extracted
sudo ad1extract -i ~/Downloads/Forensics/CorprateSec.ad1 -d /tmp/AD1_extracted -m
Différence entre ad1mount & ad1extract
| ad1mount | ad1extract | |
|---|---|---|
| Ce que ça fait | Crée une vue virtuelle via FUSE | Copie physiquement les fichiers sur le disque |
| Les fichiers existent vraiment sur le disque ? | ❌ Non, tout reste dans l'image AD1 | ✅ Oui, copies réelles créées |
| Read-only ? | ✅ Oui, forcément | ❌ Non, les fichiers extraits sont modifiables |
| Consomme de l'espace disque ? | ❌ Non | ✅ Oui (taille équivalente à l'image) |
| Accessible par Docker / autres outils ? | ❌ Problématique (FUSE) | ✅ Sans restrictions |
S'équiper pour trouver le flag (Kali linux Docker)#
mkdir -p /tmp/Forensic

# 1. Monte l'image en FUSE (lecture seule)
ad1mount -i ~/Downloads/Forensics/CorprateSec.ad1 -m /tmp/Forensic

# 2. Copie vers un répertoire Docker-accessible
mkdir -p /tmp/AD1_extracted
cp -r /tmp/Forensic/* /tmp/AD1_extracted/

# 4. Lance Exegol sur le répertoire copié
exegol start forensic -V /tmp/AD1_extracted:/mnt/forensic
Lancer un container Kali avec les fichiers montés
sudo docker run -it -v /tmp/AD1_extracted:/mnt/forensic kalilinux/kali-rolling bashOu en utilisant Exegol
exegol start forensic full -V /tmp/AD1_extracted:/mnt/forensiccd /mnt/forensicapt update && apt install regripper -yQuestions#
Q1#
Après avoir réalisé le setup, extraire le build number
cd "/mnt/forensic/DFA_SP2020_Windows.E01:Partition 2 [50649MB]:NONAME [NTFS]/[root]"regripper -r "Windows/System32/config/SOFTWARE" -p winver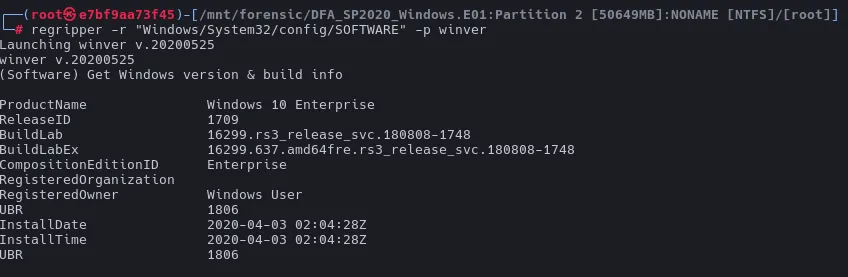
Le build number et le flag est 16299
Q2#
cd "/mnt/forensic/DFA_SP2020_Windows.E01:Partition 2 [50649MB]:NONAME [NTFS]/[root]"cd Users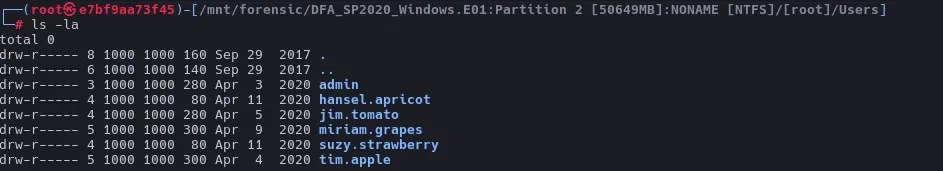
Q3#
What is the CRC64 hash of the file "fruit_apricot.jpg"?
find /mnt/forensic -type f -iname "*fruit_apricot*" 2>/dev/nullfind . -name "fruit_apricot.jpg" -exec 7z h -scrcCRC64 {} \;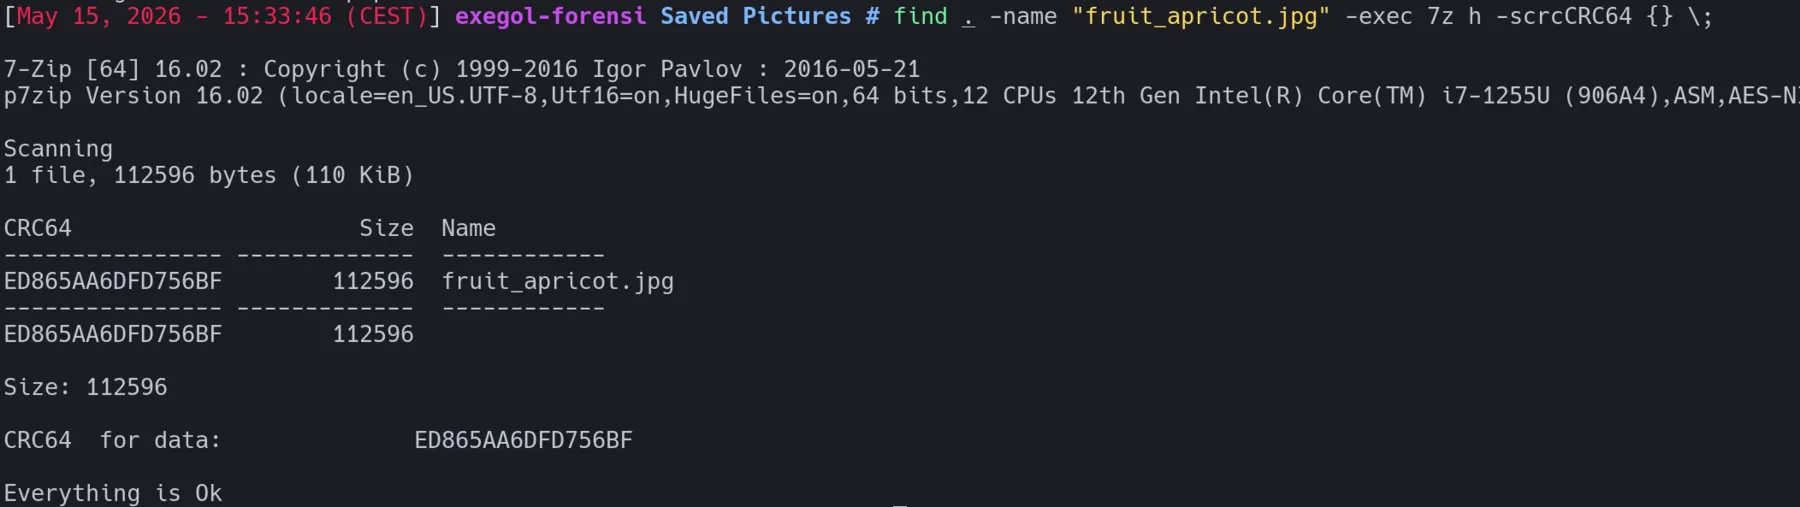
The flag is : ED865AA6DFD756BF
Q4#
What is the logical size of the file "strawberry.jpg" in bytes?
find /mnt/forensic -type f -iname "strawberry.jpg" 2>/dev/nullcd "/mnt/forensic/DFA_SP2020_Windows.E01:Partition 2 [50649MB]:NONAME [NTFS]/[root]/Users/suzy.strawberry/Pictures/"ls -laThe flag is : 72448
Q5#
What is the processor architecture of the system? (one word)
regripper -r Windows/System32/config/SYSTEM -p processor_architecture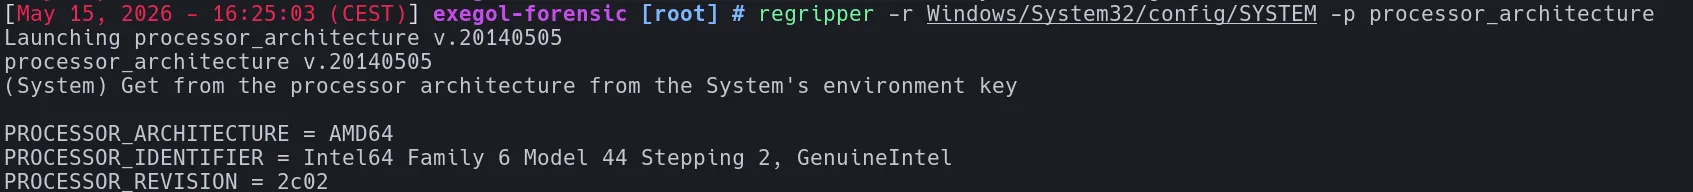
The flag is AMD64
Q6#
Which user has a photo of a dog in their recycling bin?
ls -R \$Recycle.Bin/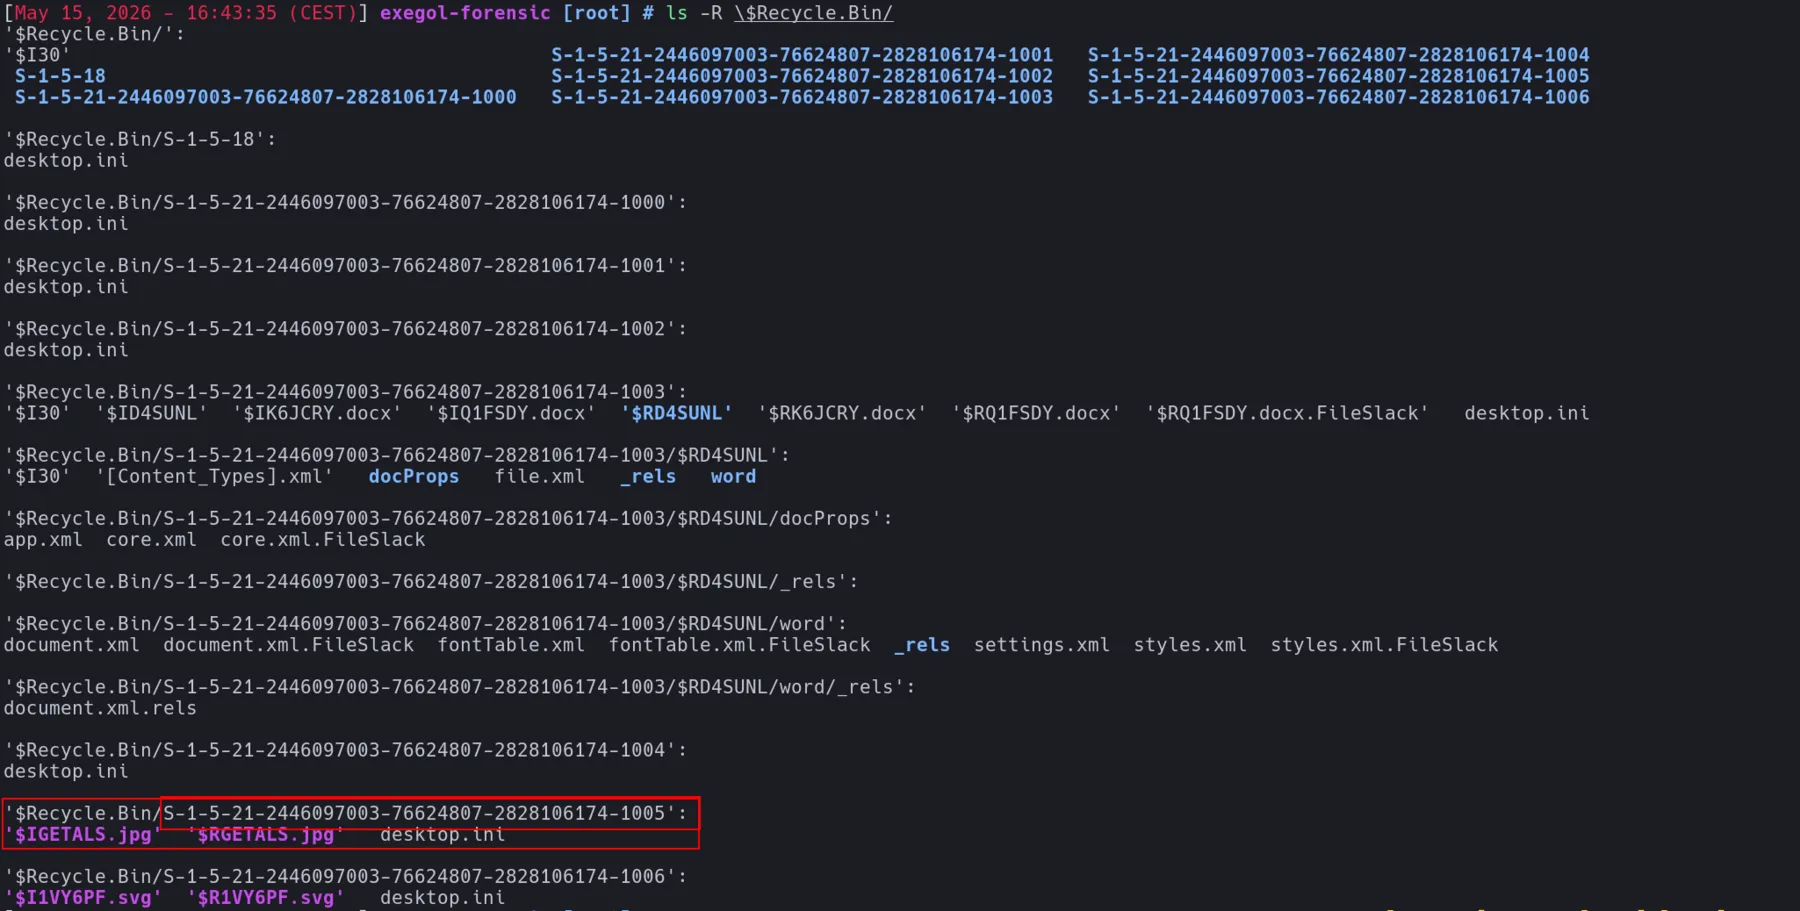
Find the SID of the users
regripper -r "/mnt/forensic/DFA_SP2020_Windows.E01:Partition 2 [50649MB]:NONAME [NTFS]/[root]/Windows/System32/config/SOFTWARE" -p profilelist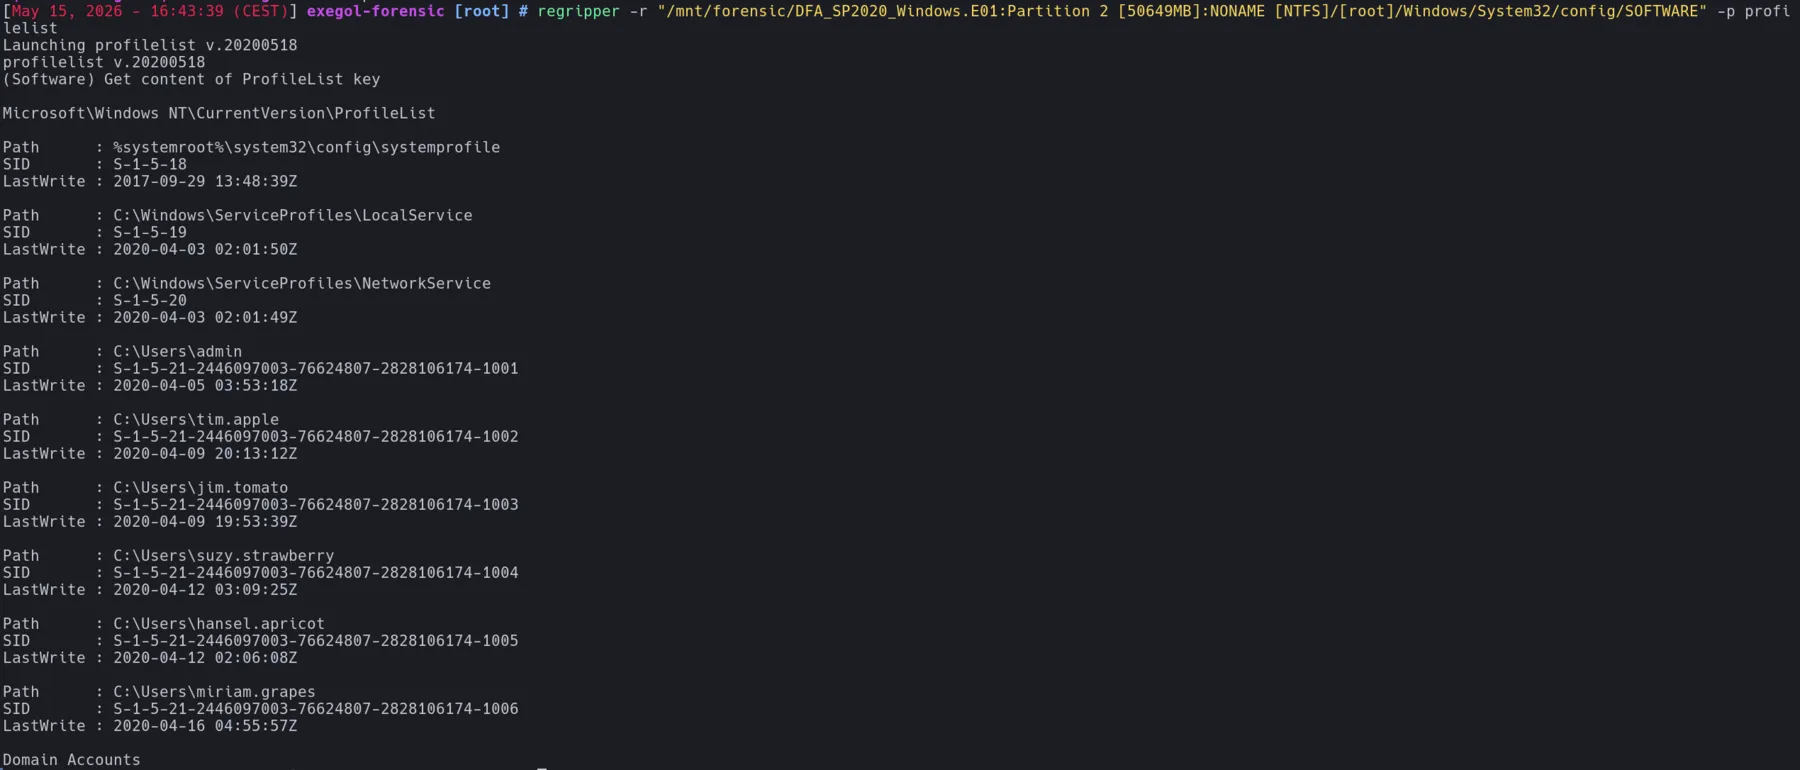
Q7#
What type of file is "vegetable"? Provide the extension without a dot.
find /mnt/forensic -type f -name "*vegetable*" 2>/dev/nullfile vegetableQ8#
What type of girls does Miriam Grapes design phones for (Target audience)?
Techniques utilisees#
- Windows Forensics (FTK Imager)
- Disk Image Analysis